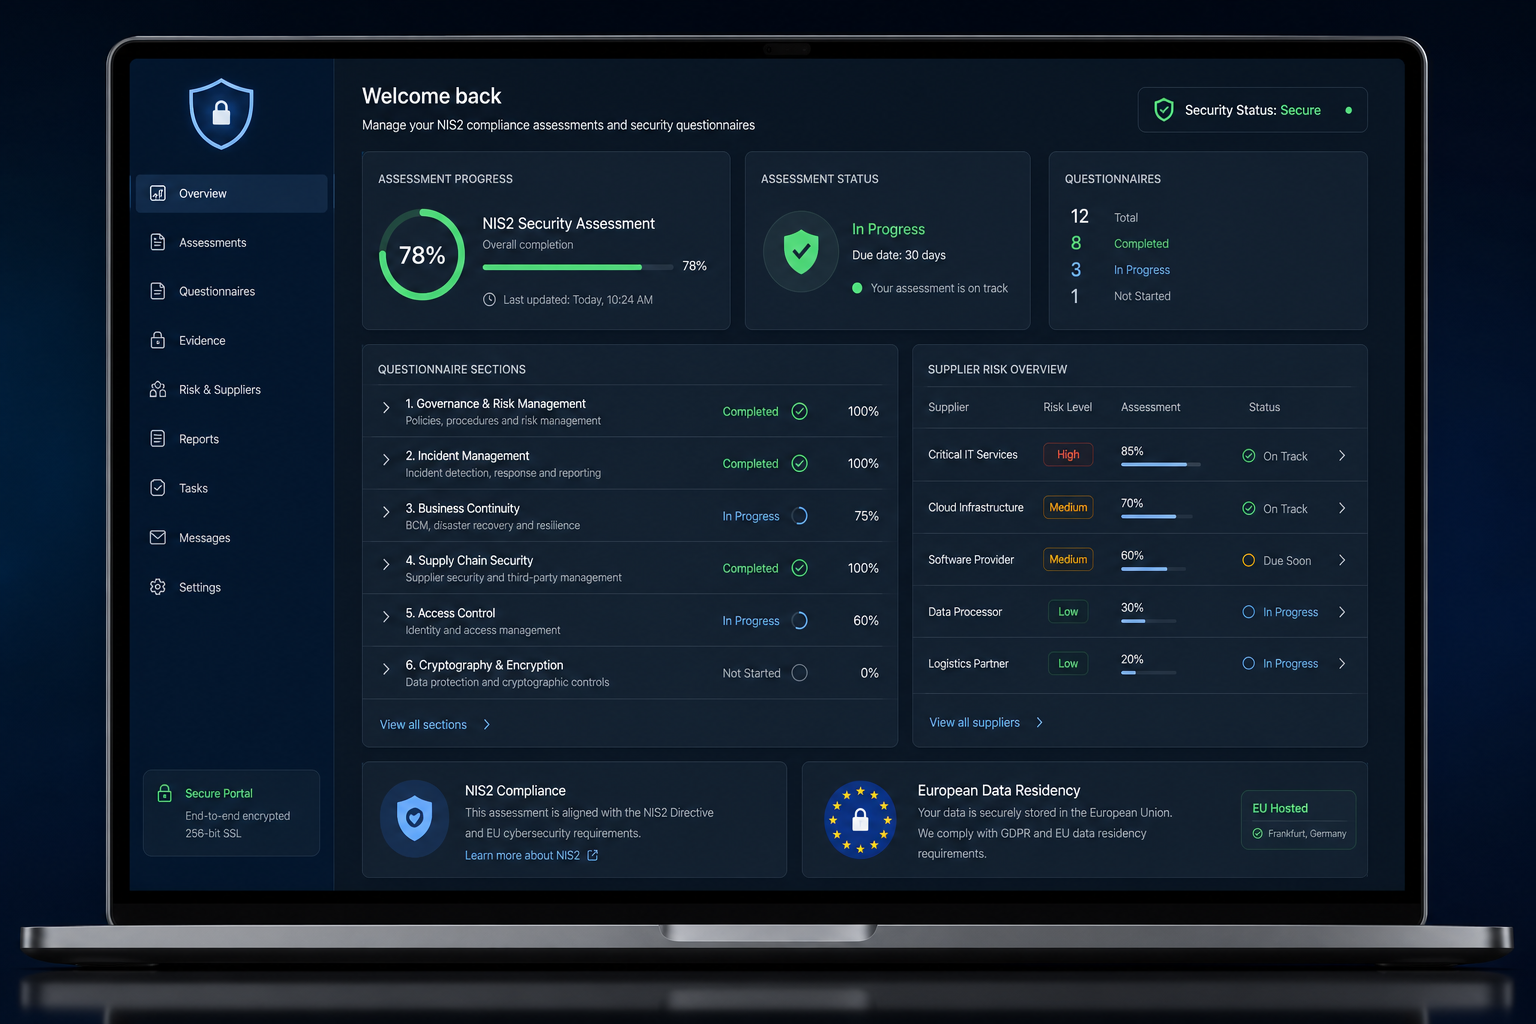
A secure portal for NIS2 challenges
IVBB wanted an accessible portal where organizations can structurally assess their cyber security and that of their suppliers. We built Samen Digitaal Veilig with security-by-design as the base principle: self-service without storing unnecessarily large amounts of sensitive data centrally.
Client
- Industry
- Cybersecurity
- Location
- Oosterhout
Team


As an association, IVBB works for stronger cyber security at Dutch organizations. For the Samen Digitaal Veilig platform we built a portal where members and related parties can use questionnaires to structurally assess their information security against NIS2 and comparable standards.
The situation
A good idea with high security requirements
The substantive vision was there, but the technical foundation was still missing. IVBB was looking for a portal where users could log in and complete questionnaires, while the risk of data leaks or traceable answers had to be kept to a minimum.
That placed strong constraints on the architecture. Sensitive data was barely allowed into their own Glossary · In briefdatabaseA database is a structured collection of data that software can store, retrieve and modify. A database management system controls access to that data.Read more, answers must not be easy to trace back to people or companies, and GDPR requirements forced all storage to stay within Europe.
The question behind the question
Further than a questionnaire tool
IVBB wanted organizations to carry out their own NIS2 assessments. The existing email process required too much manual work. The portal needed to be easy to use and store as few sensitive answers centrally as possible. We included those requirements from the design stage.
Approach
Security-by-design as guiding principle
We designed the portal knowing you can never fully rule out human error. That is exactly why we chose an architecture that deliberately spreads data across multiple systems, so a single leak does not expose everything at once.
For Glossary · In briefauthenticationAuthentication is the process by which a system verifies the claimed identity of a user, device or application.Read more and storage we leaned on AWS services, with AWS Cognito as the pivot so that a minimum of personal data has to end up in our own database. In the application database we mainly store references, additionally encrypted on top of AWS's standard security. All data stays on European servers.
The technical stack runs on a NestJS Glossary · In briefbackendThe backend is the part of an application that processes data, applies business rules and communicates with other systems on the server. Users usually access it through a frontend or API.Read more, a React Glossary · In brieffrontendThe frontend is the part of a website or application that users see and operate, such as pages, buttons, forms and interactive screens.Read more with Material UI, and GraphQL for communication between Glossary · In briefcomponentA component is a distinct part of software with its own task and a clear way of interacting with other parts.Read more. For administration we started with Strapi to get going quickly, and later moved to React Admin when requirements for the admin environment became stricter.
What we add
Minimal data exposure We limit the impact of a mistake or leak by spreading data and mainly storing references instead of keeping bulk data centrally.
Secure authentication and storage AWS, Cognito, and extra encryption form the backbone of a security-by-design approach from the first commit.
Self-service for a complex topic The portal makes a process that previously ran via email directly accessible and more scalable.
Quality and continuity
A portal that makes security practically usable
Cybersecurity has long ceased to be an exclusively technical field: usability counts at least as heavily. A solution that is technically correct but that users cannot navigate stays on the shelf. So the portal had to be not only secure; it had to work so clearly and quickly that organizations could truly get started with it themselves.
That combination of security, manageability, and ease of use made the project relevant for an association that wants to help its members strengthen their digital resilience in a concrete way.
Result
From manual process to manageable platform
The portal runs as a self-service solution. Users log in and walk through the questionnaires. That made what used to be a manual trajectory much more Glossary · In briefscalabilityScalability is the extent to which software, infrastructure or a process can handle more or less work without major rebuilding or unacceptable performance loss.Read more and pleasant, while the security requirements remained intact.
This way IVBB got a platform that supports cyber security in substance and makes it organizationally workable.
10KB dares to push back, takes responsibility, and is highly competent in the subject matter.
Antoon Scheffers — IVBB
Key takeaways
With NIS2 assessment it is not only about security on paper: organizations must be able to complete the trajectory themselves, without storing sensitive data centrally.
Spreading data across systems and storing references reduces the impact of human error or a single leak.
Security-by-design and ease of use do not have to conflict, if you take architecture choices along from day one.
OUR WORK